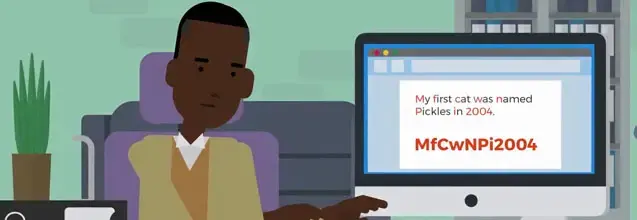
Information security compliance training helps employees protect sensitive business and client data, prevent security breaches and safeguard customer trust. Most security incidents start with everyday actions, not sophisticated technical failures so it's important for staff to be able to recognise threats and handle information securely to protect the business. Our in-depth Information Security Compliance Training Course explains the importance of information security, the consequences of a breach, how to classify information correctly, and how to use the internet and email securely.
Give your workforce the knowledge they need to reduce avoidable risks. This CPD UK accredited information security compliance e-learning enables your organisation to reinforce secure working practices and demonstrate your commitment to information security compliance.
What you’ll learn in this course
Understand why information security is critical to our business
Recognise the consequences of data breaches
Learn how and why information is classified
Exercise caution when using the internet, emails and other electronic communications
Comply with Company procedures in relation to network access, portable media and devices, and physical security
Know how and when to report actual or suspected data breaches
Hear from our customers
We've been using Skillcast for approx. 1.5 years and have been very happy with the service received and the courses offered. The customer service from the support team is excellent, they always respond quickly and are very helpful. The courses offered cover a broad range and the FCA courses were particularly useful to our business.
Feefo Customer Rating ★★★★★4.9/5
Ready to try this course?
Start your free trial of this course and get instant access today.
Operational resilience is essential for financial services firms during unexpected disruptions. This in-depth course for UK staff explores regulatory compliance requirements set by the FCA and PRA, plus foundational pillars and concepts such as cyber resilience, operational risk, important business services, operational disruptions and impact tolerances. Employees will learn how business continuity and disaster recovery contribute to an effective resilience framework, alongside the role of scenario testing, mapping of business processes, and assessing critical third-party providers (CTPs). The course also covers implementation and governance processes UK firms must keep in mind, from self-assessment documentation and communication strategies to lessons learned exercises.
Operational Risk
In-depth50 MinutesRisk ManagementFor all staff
Leaders will explore how operational risk is defined and how organisations identify, assess and monitor risks. The course covers risk assessments and indicators, controls, scenario analysis and the different approaches available for managing risk, including mitigation, transfer and acceptance.
Business Continuity Management
In-depth40 MinutesRisk ManagementFor all staff
Some disruptions are unavoidable. Being unprepared for them is not. Our Business Continuity Management Training explains how to identify and analyse risks, develop effective continuity plans and prepare for disaster recovery. Equip employees with the knowledge to respond confidently under pressure, minimise disruption and help protect essential business activities. This in-depth compliance course supports a more resilient organisation, helping teams turn continuity plans into practical action.
Information Security Compliance Training Course
In-depth35 MinutesFor all staff
Information security compliance training helps employees protect sensitive business and client data, prevent security breaches and safeguard customer trust. Most security incidents start with everyday actions, not sophisticated technical failures so it's important for staff to be able to recognise threats and handle information securely to protect the business. Our in-depth Information Security Compliance Training Course explains the importance of information security, the consequences of a breach, how to classify information correctly, and how to use the internet and email securely. Give your workforce the knowledge they need to reduce avoidable risks. This CPD UK accredited information security compliance e-learning enables your organisation to reinforce secure working practices and demonstrate your commitment to information security compliance.
Digital Operational Resilience Act (DORA)
In-depth25 MinutesFor all staff
DORA rests on information and communication technology (ICT) risk management. Firms identify the systems they depend on, conduct risk assessments and put controls in place to protect operational integrity. Resilience testing shows whether the defences hold, and incident reporting and incident response set out what happens if they don’t. Suppliers come next: third-party risk and due diligence on third-party providers sit at the centre of the Digital Operational Resilience Act. Meanwhile, employee awareness helps stop cyber threats.
Electronic Communications
In-depth25 MinutesFor all staff
Business communications are disclosable in litigation and reviewable by regulators, and the informal register people use in chat tools does not read well years later out of context. Recording and retention obligations also extend to channels many staff assume are private. Setting the expectation clearly protects individuals from a message written quickly and protects the firm from having to explain it.
Digital Operational Resilience Act (DORA)
In-depth25 MinutesFor all staff
A cyberattack on a bank’s payment system can disrupt customers and firms across several countries. The Digital Operational Resilience Act (DORA) sets out how financial entities must withstand, respond to and recover from those kinds of issues. This in-depth compliance course helps UK staff understand what DORA requires and why it matters to firms that serve EU customers or work with EU partners. DORA begins with ICT risk management: knowing which systems a firm depends on, conducting risk assessments, and protecting operational integrity. Resilience testing checks the defences work, while incident reporting and incident response set out what happens when they don’t. Understand why third-party risk is a major focus, how due diligence on third-party providers fits in, and why employee awareness is a key line of defence.
Cybersecurity
In-depth20 MinutesFor all staff
Employees will explore common threats, warning signs and practical security measures that help protect systems, data and business operations. The course also explains how to report incidents, access internal support and follow organisational procedures when concerns arise.
Records Management
In-depth20 MinutesFor all staff
Train staff to manage records responsibly, protect sensitive information and meet record-keeping obligations. This practical records management compliance e-learning helps employees understand their responsibilities, make informed retention decisions and dispose of records appropriately. Close the gap between your documented procedures and everyday practice to reduce compliance risks and keep your records management processes fit for purpose.
Information Security
Refresher20 MinutesCybersecurityFor all staff
Security behaviour degrades between annual courses, and attackers rely on that. A short refresher keeps classification habits and email caution current without repeating the full course, which makes it practical to run more than once a year. For firms subject to DORA or regular client security assessments, a documented refresher cycle is increasingly what evidence of ongoing awareness actually means.
Cybersecurity Compliance Training Course
Express20 MinutesCybersecurityFor all staff
Attackers target people because people are reachable and predictable under time pressure. The short format matters here: cyber awareness works best delivered frequently rather than thoroughly once a year, since the techniques change faster than annual training cycles. Running this across the whole workforce gives you a control that scales, and satisfies the staff awareness expectations that appear in client and supplier security assessments.
Phishing
Express15 MinutesCybersecurityFor all staff
Phishing is how most breaches begin, and the messages have improved enormously with better tooling behind them. The decisive factor is rarely whether someone clicked but how quickly they said so. Training that removes the embarrassment around reporting shortens that gap, and short modules can be repeated often enough to keep pace with techniques that change every few months.
Think Before You Click
Microlearning5 MinutesCybersecurityFor all staff
Clicking on malicious links or attachments is one of the most common ways cybercriminals infect IT systems with malware. This training helps employees recognise suspicious emails, understand the dangers of phishing and ransomware and apply best practices to protect company data.
Guide to Secure Remote Working
Microlearning5 MinutesCybersecurityFor all staff
Remote work provides flexibility but also introduces cybersecurity risks that can compromise company data and systems. This training helps employees understand the security challenges of working from home and apply best practices to protect sensitive information.
CEO Fraud
Microlearning5 MinutesCybersecurityFor all staff
CEO fraud is a type of Business Email Compromise where cybercriminals impersonate executives to trick employees into making payments or sharing confidential information. This training helps employees recognise CEO fraud attempts, understand spoofing tactics and follow verification steps to prevent financial and data loss.
Advising Customers on Cybersecurity
Microlearning5 MinutesCybersecurityFor all staff
Cybersecurity is everyone's responsibility, including guiding customers to protect themselves from online threats. This training helps employees understand common cyber risks customers face and how to provide clear, helpful security advice to build trust and prevent fraud.
Using Wi-Fi safely
Microlearning5 MinutesCybersecurityFor all staff
Wi-Fi connectivity offers convenience but also exposes devices and data to security risks if not properly managed. This training helps employees understand Wi-Fi security threats and apply best practices to protect sensitive information when working from home, in the office and on the move.
Transferring Information Securely
Microlearning5 MinutesCybersecurityFor all staff
Securely transferring information is essential to protect sensitive data from breaches, legal risks and business disruptions. This training helps employees understand best practices for secure communication, including encryption, password protection and using secure transfer protocols.
Supply Chain Cybersecurity
Microlearning5 MinutesCybersecurityFor all staff
A company’s cybersecurity is only as strong as its weakest link and supply chain vulnerabilities can expose businesses to major breaches. This training helps employees understand the risks posed by third-party access, the importance of supply chain security and best practices to prevent cyberattacks.
Secure Web Browsing
Microlearning5 MinutesCybersecurityFor all staff
Practicing safe web browsing helps to reduce security risks and protect sensitive information. This training explains how to browse the internet securely and avoid common cyber threats.
Tailgating and Piggybacking
Microlearning5 MinutesCybersecurityFor all staff
Cybersecurity is not just about digital protection but also involves securing physical access to critical systems. This training helps employees recognise security risks like tailgating and piggybacking, understand their consequences and take steps to prevent unauthorised access.
Information Security on the Move
Microlearning5 MinutesCybersecurityFor all staff
Handling company information securely, especially when working remotely or traveling, is essential to prevent data breaches and security risks. This training helps employees understand how to protect sensitive information, secure devices and minimise exposure to cyber and physical threats.
Information Classification
Microlearning5 MinutesCybersecurityFor all staff
This training helps employees understand different levels of information classification, their restrictions and how to handle data securely.
Reacting to Password Breaches
Microlearning5 MinutesCybersecurityFor all staff
Password breaches can lead to unauthorised access, fraud and data theft, often resulting from weak passwords, phishing or insecure networks. This training helps employees recognise the warning signs of compromised credentials, understand the risks and apply best practices to prevent breaches.
Multi-factor Authentication
Microlearning5 MinutesCybersecurityFor all staff
Multi-factor authentication (MFA) enhances security by requiring users to verify their identity through multiple authentication methods. This training helps employees understand the importance of MFA, how it protects company data and when it should be used.
Creating Strong Passwords
Microlearning5 MinutesCybersecurityFor all staff
Strong password protection is essential to safeguarding company systems from cyber threats such as brute force attacks and password guessing. This training helps employees understand the importance of creating strong passwords, following security policies and preventing unauthorised access.
Vishing
Microlearning5 MinutesCybersecurityFor all staff
Vishing is a social engineering attack where cybercriminals use phone calls to trick individuals into revealing sensitive information. This training helps employees recognise vishing attempts, understand manipulation tactics and apply best practices to verify callers and protect confidential data.
Video Conferencing
Microlearning5 MinutesCybersecurityFor all staff
Video conferencing is a vital business tool, but it also presents security and privacy risks if not used correctly. This training helps employees understand best practices for secure video meetings, from using approved software to protecting confidential information.
Spear Phishing
Microlearning5 MinutesCybersecurityFor all staff
Spear phishing targets specific individuals with convincing emails designed to deceive them. This training demonstrates how to recognise and handle these targeted phishing attempts.
Smishing
Microlearning5 MinutesCybersecurityFor all staff
Smishing is a targeted phishing scam that uses deceptive text messages to gain sensitive information. This training highlights how to recognise and avoid falling victim to smishing attacks.
Ransomware
Microlearning5 MinutesCybersecurityFor all staff
Ransomware is a type of malware that encrypts files and demands payment for their release, often causing severe financial and operational damage. This training helps employees recognise ransomware threats, understand how attacks occur and take preventive measures to protect company systems.
Malware
Microlearning5 MinutesCybersecurityFor all staff
Malware is malicious software designed to harm or exploit computer systems, ranging from viruses and ransomware to spyware and botnets. This training helps employees recognise different types of malware, understand how they spread and take proactive steps to prevent infections.
Device Hygiene
Microlearning5 MinutesCybersecurityFor all staff
Device hygiene is the practice of keeping digital devices secure and free from cyber threats to protect company data and networks. This training helps employees understand the importance of device hygiene and apply best practices to prevent malware infections, data breaches and unauthorised access.
Bring Your Own Device Security
Microlearning5 MinutesCybersecurityFor all staff
Bring Your Own Device (BYOD) policies offer convenience and flexibility but also introduce cybersecurity risks. This training helps employees understand the precautions necessary to secure personal devices and protect company data from threats like theft, hacking and data breaches.
Zero Trust Cybersecurity
Microlearning5 MinutesCybersecurityFor all staff
The zero trust cybersecurity model ensures IT systems remain inaccessible by default, requiring strict verification before granting access. This training helps employees understand how zero trust works, including authentication measures, restricted access and continuous security monitoring.
Common Cyber Threats
Microlearning5 MinutesCybersecurityFor all staff
Cyber threats such as phishing, malware, ransomware and unsecured networks pose significant risks to businesses. This training helps employees recognise common cyber threats, understand their impact and apply best practices to prevent security breaches.
Understanding Information Security
Microlearning5 MinutesCybersecurityFor all staff
Information security is essential to protect sensitive business and customer data from unauthorised access, breaches and cyber threats. This training helps employees understand their role in safeguarding information, following security policies and identifying potential risks.
Deepfake Awareness
Microlearning5 MinutesCybersecurityFor all staff
Deepfakes use artificial intelligence to create fake images, audio or videos that can deceive individuals and organisations. This training helps employees recognise deepfake scams, understand their risks and apply verification steps to prevent fraud and cybercrime.
Business Email Compromise
Microlearning5 MinutesCybersecurityFor all staff
Business Email Compromise (BEC) is a targeted cyberattack where criminals impersonate executives or hack accounts to steal money or sensitive information. This training helps employees recognise different types of BEC scams, understand the risks and apply verification steps to prevent fraud.
Spot a Phishing Attempt
Microlearning5 MinutesCybersecurityFor all staff
Phishing emails are fraudulent attempts by cybercriminals to trick individuals into revealing sensitive information. This training helps employees recognise phishing attempts, identify red flags in emails and take steps to protect personal and company data from cyber threats.